There is no need to install any anti-malware application on Windows 8 and newer versions of Windows, since Windows Defender is installed by default. This built-in security suite is enough to provide primary protection for your PC and also keep you safe online.
When trying to enable Windows Defender, you may get the following error: ‘This app is turned off by group policy’ and this is caused by two main reasons: If your PC is part of a domain and the domain controller assigned some policies, Windows Defender may get blocked. In other cases, if you’ve installed a 3rd party antivirus, it is like to block Defender and the block may remain active even if you’ve uninstalled the application. In such a condition, when you try to enable defender, you’ll get the error as shown in the image above.
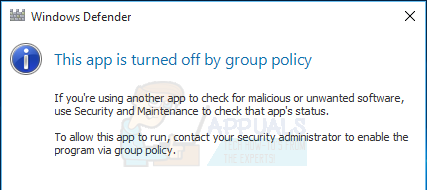
This error is largely fixed by asking your system administrator to enable Windows Defender via Group Policy. You can also fix this by turning it on with the Local Group Policy Editor or applying a registry tweak.
Method 1: Enabling Windows Defender Using the Local Group Policy Editor
Before you proceed with this method, note that the Local Group Policy Editor is only available in Windows Enterprise and Pro Editions.
To fix this issue follow the steps below:
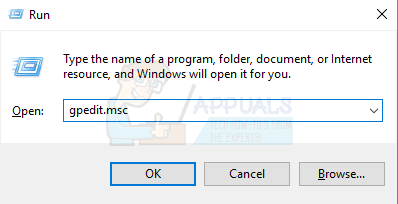
- Press the Windows Key + R, type in gpedit.msc in the Run dialog box and click OK to open the Local Group Policy Editor. (If gpedit) is not available on your system, then use this guide gpedit to install it.
- In the Local Group Policy Editor, navigate to Computer Configuration > Administrative Templates > Windows Components > Windows Defender.
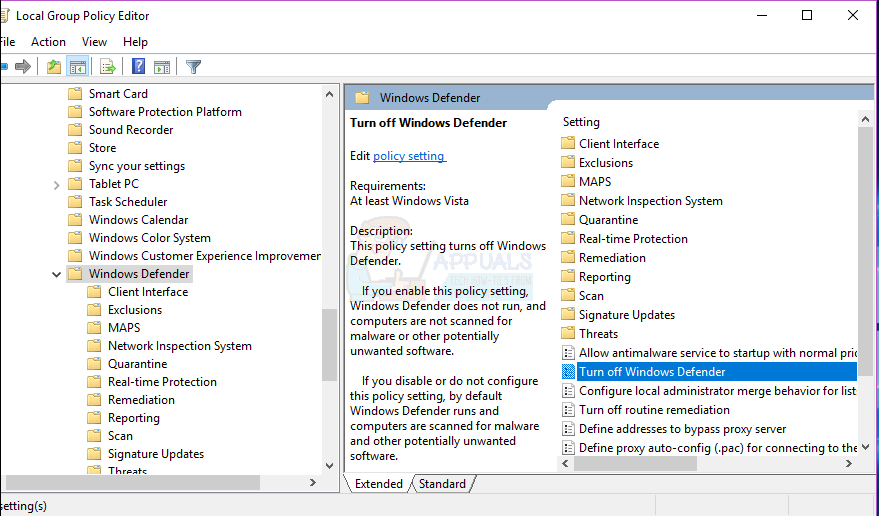
- At this Group Policy path, look for the setting named Turn off Windows Defender and double click it. Select either the Not Configured or Disabled option to enable Windows Defender. Click Apply followed by OK.

- Close the Local Group Policy Editor and then restart the computer. After rebooting, try to enable Windows Defender, it should work.
Method 2: Remove Existing Anti-Malware Software
If you PC still has another antivirus installed or if one was just uninstalled, you should use the appropriate tool to remove all 3rd party antivirus and antispyware applications.
To fix this issue follow the steps below:
- Using your browser, download the removal tool from your antivirus software using the links below.
You can also use the AppRemover feature in the OESIS Endpoint Assessment Tool to remove multiple anti-malware products (not listed here).
- Launch the downloaded utility and follow its prompts to completely remove the anti-malware application from your system.
- Reboot your PC.
- Try to enable Windows Defender now.
Method 3: Restart the Security Center Service
Restarting the Security Center Service can help in solving the problem.
To fix this issue follow the steps below:
- Press the Windows Key + R, type in services.msc in the Run dialog box and click OK to open the Windows Services Console

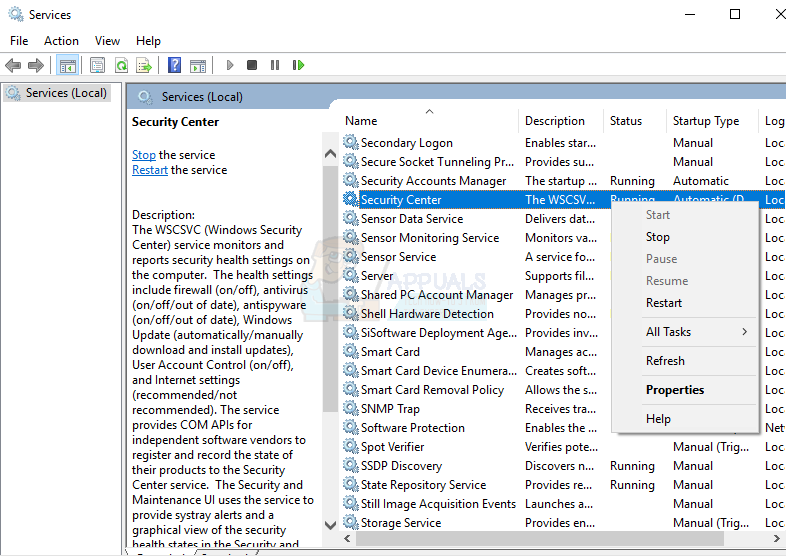
- In the Services console, search for ‘Security Center’
- Right click on ‘Security Center’ and then click on Restart.
Method 4: Enabling Windows Defender From the Registry
It is important to note that you have to proceed with this method only after trying the above steps. Editing your registry can cause undesirable effects. Windows disables Defender if it detects the presence of another anti-malware software. This can be enabled in the registry, but ensure that there are no conflicting softwares and Windows is not infected.
To fix this issue follow the steps below:
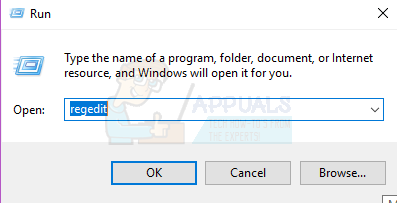
- Press the Windows Key + R, type in regedit in the Run dialog box and click OK to open the Windows Registry.
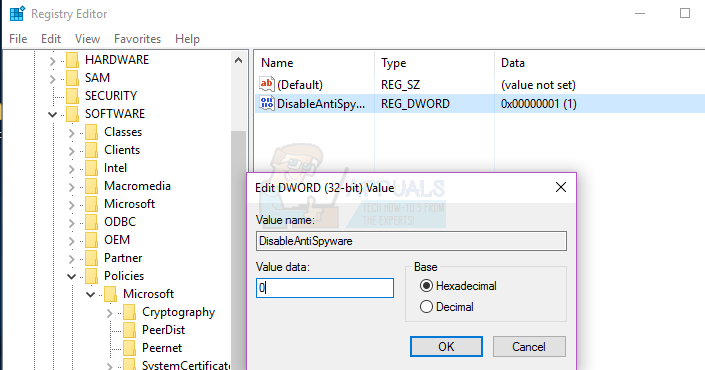
- In the Registry Editor, navigate to HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender
- If you see a registry entry named DisableAntiSpyware, double click to edit it and change its value to 0. It’s normal if you don’t find this registry key and you don’t have to do anything.
Method 5: Deleting Conflicting Registry entries
Some malwares may add malicious keys into the registry to block active antiviruses from running. You can find and delete them from the registry using these steps:
- Press the Windows Key + R, type in regedit in the Run dialog box and click OK to open the Windows Registry.
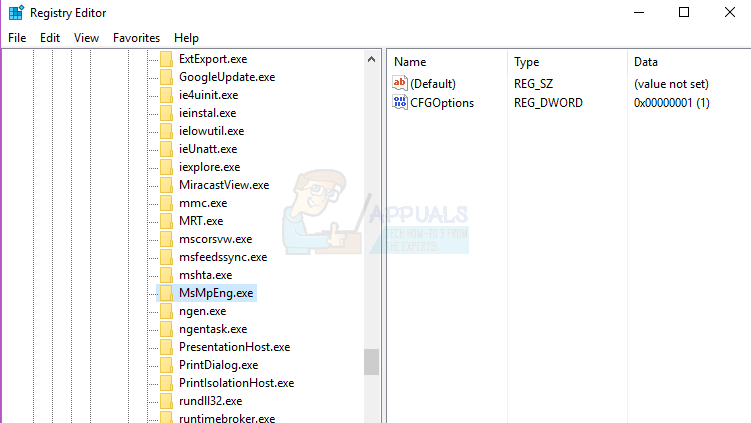
- In the Registry Editor, navigate to HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution Options
- In this key, look for the following entries. MSASCui.exe, MpCmdRun.exe and MsMpEng.exe. If you find any of these entries, right click on it and select Delete. It’s normal if you don’t find these registry entries hence you don’t have to do anything.
Comments
Post a Comment